Blog
Practical guidance for building a stronger, more resilient security program.
CMMC Phase 2 Is Suspended — Here's What Defense Contractors Should Actually Do Right Now
If you've been bracing for CMMC Level 2 third-party certification requirements to hit your contracts this November, you can exhale a little. On July 13, 2026, the Department of War suspended the rollout of CMMC Phase 2, the stage that was set to require independent C3PAO assessments for many contractors handling Controlled Unclassified Information (CUI).
Read article
CMMC Phase II Just Got Suspended — Here's What Defense Contractors Should Do Right Now Instead of Waiting
The landscape of the cyber security maturity model certification (CMMC) has undergone a significant shift. On July 13, 2026, the Department of Defense (DoD) announced a formal suspension of CMMC Phase II implementation milestones.
Read article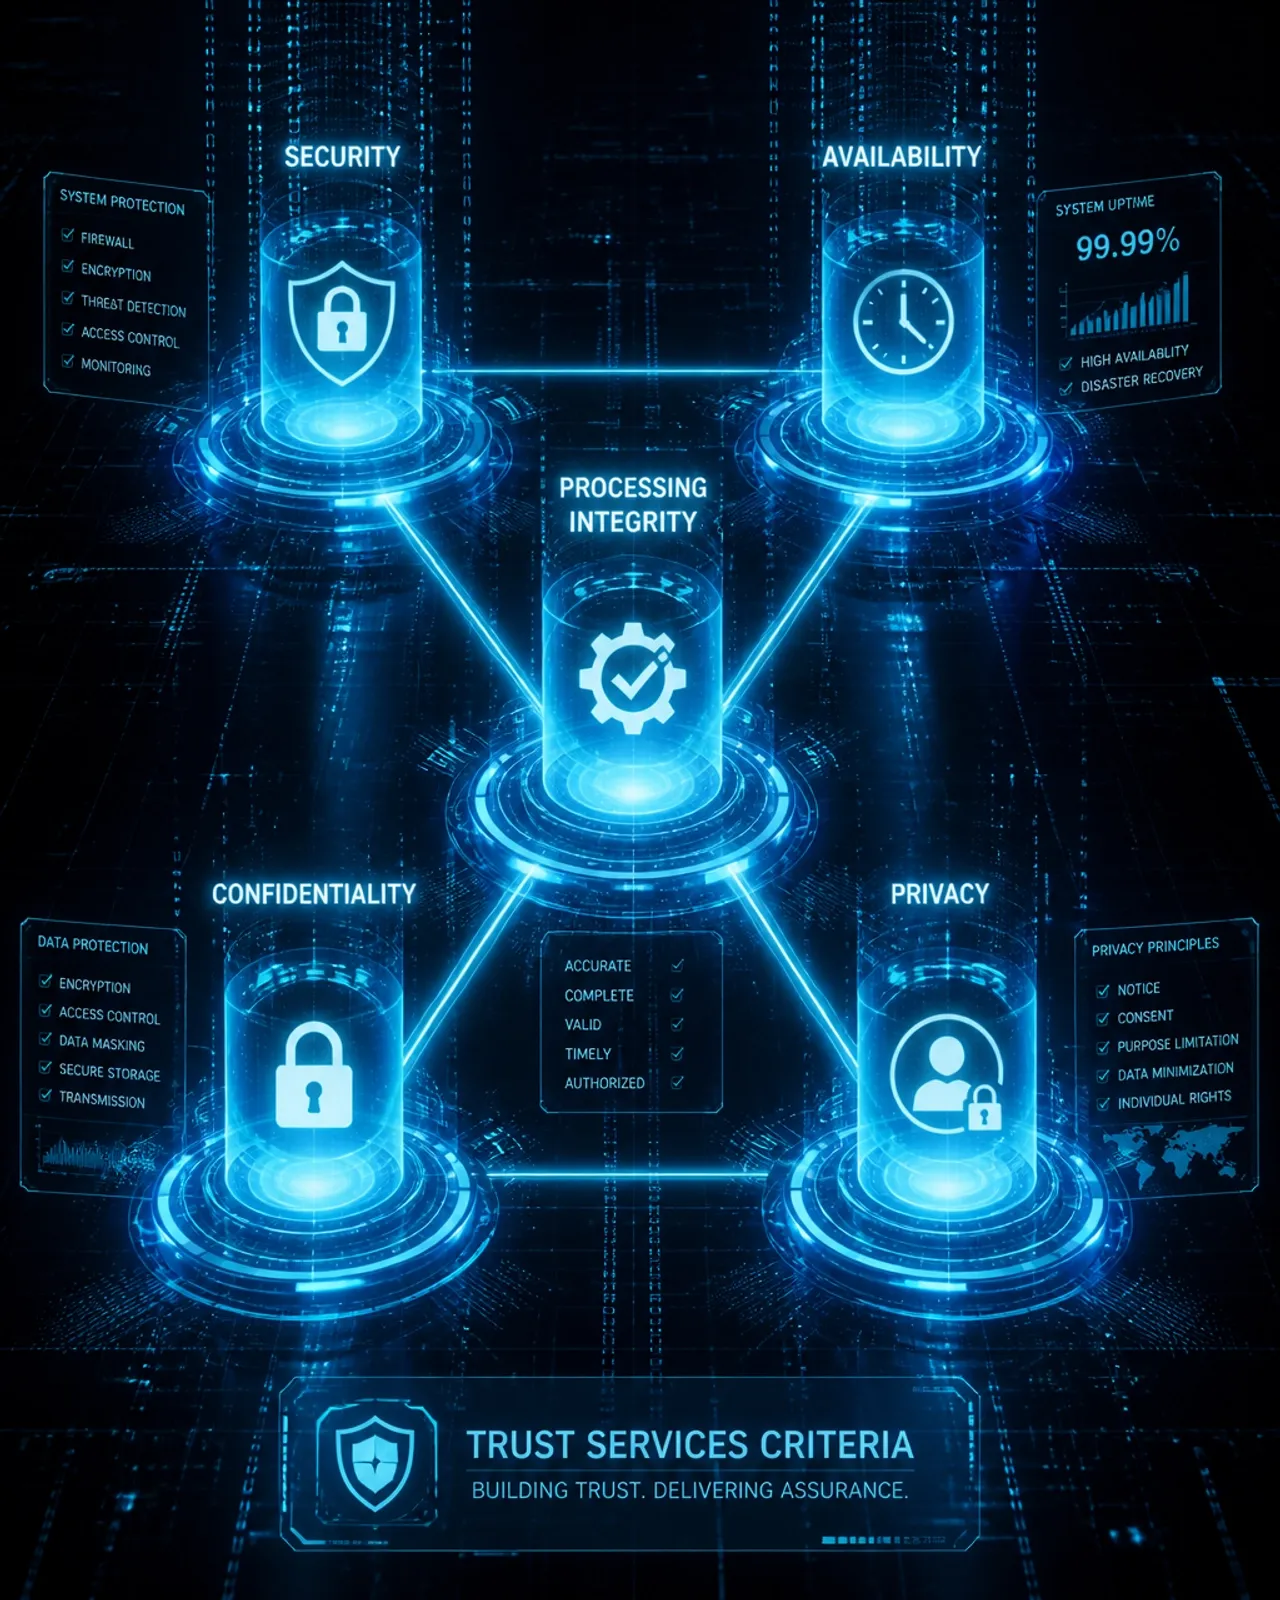
The Ultimate Guide to SOC 2 Compliance
In the contemporary digital landscape, where data serves as the lifeblood of global enterprise, the concept of "trust" has transitioned from a qualitative attribute to a measurable, high-stakes asset.
Read articleHow to Choose a Cybersecurity Consulting Firm: 7 Questions That Separate the Experts From the Pretenders
Choosing among cybersecurity consulting firms is not simply a matter of comparing hourly rates, certifications, or the length of a proposal. The right partner must understand how your organization operates, identify the risks that could materially affect your business, and translate technical findings into a practical plan.
Read article
From Scans to Strategy: Building a Vulnerability Management Program That Actually Reduces Risk
A vulnerability scan can identify weaknesses, but it cannot determine which findings deserve immediate executive attention, which systems support critical business processes, or which remediation actions will reduce the greatest amount of risk.
Read articleDoes Your Business Need a CCPA Cyber Audit? How to Get Audit-Ready Before January 1, 2027
California's updated CCPA regulations create a new annual cybersecurity audit obligation for certain for-profit businesses that process California consumers' personal information and whose processing presents a significant risk to consumers' security.
Read article
2026-10-16T13:05:51.632Z
You Patched Citrix NetScaler. You're Still Exposed. Here's What Nobody Tells You About Patch Validation.

2026-10-10T12:56:41.558Z